
Ban on AI Tools
A rule that forbids staff from using AI tools for work, either outright or tool by tool. A blanket ban removes the approved route but not the task, so use tends to move onto personal accounts the business cannot see.
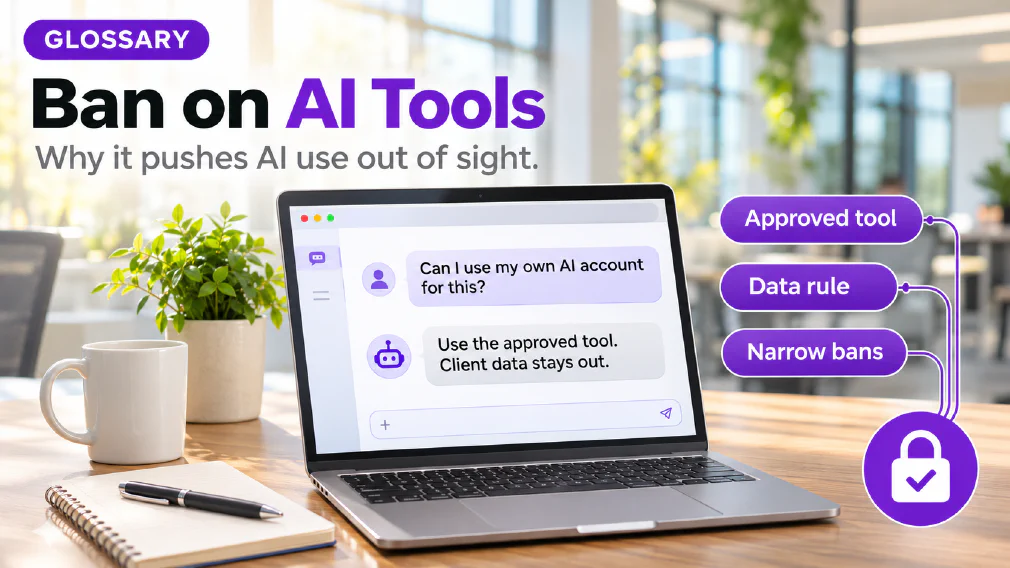
What a ban on AI Tools means
A ban on AI tools is a rule that forbids staff from using AI for work. It can be one sentence (“no AI tools”) or a list of tools blocked one at a time. It is the most common instinct when a manager finds someone pasting work into a chatbot, and it feels like the safe choice.
The banning article shows why it rarely is. A ban removes a tool but not the task. The client email still needs an answer by five o’clock, and the long report still needs summarising before tomorrow’s meeting. The person facing that deadline has a personal account already set up, so the work moves there. The risk has not gone down. The business’s view of it has, and what is left is shadow AI.
Does a ban stop staff using AI Tools?
Usually not, and the surveys the site relies on point the same way. An accountancy firm’s survey of more than 1,000 employees found that 28% said they would use AI at work even if it were banned, and that 60% of workers rely on consumer AI platforms rather than tools their company provides. A survey of 25,000 UK workers by a professional services firm, reported in the trade press, found that almost one in ten had used an AI tool their employer had banned or would disapprove of. The reporting does not say how many of those workers were under a formal ban, so the banning article treats that figure as a floor for hidden use and not a full count.
The same pattern shows up in what people enter. In a July 2026 survey of 500 employed US adults, run by a law firm, 38% admitted entering at least one type of work information into a personal AI account their employer does not control. Some 23% had pasted in internal emails, memos or documents. Another 11.8% had entered customer or client information, 11.4% contracts or legal documents, and 10.6% employee or HR information.
All of these surveys are self-reported and were run by commercial firms, so read them as direction and not as precise measurement. The direction is consistent. People use AI because it is useful, and without an approved option they use whatever is closest.
Why most Businesses do not have one
The picture most managers carry is a workforce that was told no and is quietly saying yes. The data describes something different. In the law firm’s survey, only 6.6% said their employer bans AI tools outright, and only 35.8% said their employer has a clear written policy on what work information may be shared with AI. Forty per cent said no such policy exists, and another 24.2% were not sure. That leaves 64.2% improvising.
The accountancy survey points the same way. It found 36% of workers said their company has a formal AI policy, and only 22% said their employer actively monitors AI use. So the real choice in most workplaces is not between a ban and permission. It is between a rule and silence, and a blanket ban is an answer to a problem most small businesses do not have.
A ban also has no clear edge. The banning article notes that generative AI now sits inside email clients, meeting software, document editors and browsers, often switched on by default in products the business already pays for. A rule written as “no AI tools” leaves staff guessing where it stops.
What a blanket ban gets wrong
It treats every use the same, and the uses are not the same. Rewriting a paragraph that is already public carries almost no risk. Pasting in a client contract carries a lot. When a rule refuses to tell those apart, staff learn that the rule is crude, and people discount crude rules. The one distinction that matters, which data is safe and which is not, is the one a ban never teaches.
It also invites quiet exceptions. A ban that managers bend because a deadline needs the work done teaches the team two things at once: the rule can be ignored, and the way to ignore it is to say nothing. Both lessons are hard to reverse once they set, and repeating the ban more firmly does not undo them.
The last effect is on reporting. When all use is prohibited, a person who pasted the wrong document into a personal account has every reason to stay quiet, and the business hears about it later, usually from a client. The banning article’s point is that a rule treating all use as misconduct makes the honest report the riskiest thing an employee can do. That is how a small mistake becomes a serious one.
Why a ban hides the Risk
Use on a company-approved tool can be reviewed, logged and improved. Use on a personal account on a personal phone leaves no record anywhere the business runs. The risk has not gone down. The visibility has.
The customer data article adds a quieter point. A conversation history kept in a personal account is a copy of whatever was typed, sitting in an account the business does not control, and it will still be there when that person leaves the company. The same assistant also behaves differently under a personal login and under a business agreement: where the data goes, how long it stays, whether it trains a model, who can read it and whether it comes back. The business can only set those terms on an account it owns.
The shadow AI page puts the distinction in one line: the word that matters is not “unauthorised” but “reviewed”. A tool the business has approved on a business account, with its data terms read and an owner named, is not shadow AI. The same tool through a personal login is.
What to put in place of a ban
The banning article sets out five steps, and the first two can be in place quickly.
- An approved tool that is good enough, on a business account where data-handling and retention settings are under the business’s control. If the approved option is slower or weaker than the personal one, people keep using the personal one. Test it on the tasks staff actually do before announcing it.
- A line drawn by kind of data, not by tool. One page in plain language saying what may never be entered, what is fine in the approved tool, and who to ask about anything else.
- The reason behind each line. A rule people understand gets followed in cases it did not anticipate, which is where most real decisions happen. That is what AI literacy is for.
- Ask before you audit. A short, no-blame conversation with each team about what they use and what the approved tool lacks. Listing by asking reaches the personal accounts a technical scan cannot, and the answers are a list of needs the approved tool has to meet.
- An owner and a review date, so the rule does not go stale as new tools and features arrive. See AI ownership.
The tool list that comes out of step four is the AI tool inventory: a single page of tool, user and purpose, often the first time anyone has seen the whole picture.
The one-page Data rule
The use policy guide offers a three-tier rule that fits in a small table and gives the same answer to everyone.
| Tier | What it covers | The rule |
|---|---|---|
| Never | Passwords and access keys, payment details, health information, anything under a confidentiality agreement, unredacted customer records | Never goes into any AI tool |
| With care | Anything that identifies a person, internal financial figures, draft contracts, unpublished plans | Only in an approved tool, with names and identifiers removed where possible |
| Safe | Published material, public information, your own generic text, and tasks with no names or confidential detail | Fine in an approved tool |
Client and HR data is what a business’s data protection duties already cover, so the page adds no new principle. It makes an existing one usable on a busy afternoon. The approved list should also say which version of a tool is approved, not only its name, because many consumer versions keep what you type and business versions often do not. For sorting data into tiers in the first place, see data classification.
When a Narrow ban is Right
None of this argues against ever prohibiting anything. It argues against prohibiting everything with one sentence.
A specific tool can be wrong for a specific kind of data. If a consumer service’s terms let it keep and reuse what you enter, and you handle client material under confidentiality, that tool should be off the table for that material. Say so by name. Regulated data is another case: where the GDPR applies to the personal data involved and no approved tool with suitable terms exists yet, the honest answer is not to use AI on that data until one does. Certain uses also fall under the EU AI Act, which restricts some practices and imposes obligations on others according to what the system does, not how large the organisation using it is. Those need a classification before anyone uses them, and that is a decision for the person who owns the rule, not for each employee.
A good narrow ban does four things. It names the tool or the data. It gives the reason in a sentence. It points to the approved alternative. It says who to ask when a case is unclear. A rule with those four parts is one people can follow, and one a manager can defend if a client asks why.
Keep the list short and dated. Every entry should carry the reason it exists and a review date, because the reason often expires: a tool whose terms were unacceptable last year may have changed them, and an approved alternative that did not exist in spring may exist now. A ban list that only grows becomes the same blanket prohibition by accumulation, and staff will treat it the same way.
A worked example
An illustration, not a case study. A professional services SME of about twenty-five people finds that two colleagues have been summarising client calls in a personal AI account.
Under a ban, the owner sends a warning email. The summaries carry on, now on phones, and nobody says so. Under the approach above, the owner asks the two people what the summaries are for and learns that follow-up notes take an hour after every call. The owner then approves a tool with a meeting-summary feature and data terms that suit client material, on a business account, and the one-page rule says call content goes in only through that tool. One narrow ban is added: the consumer chatbot the two had been using is off the table for client material, with a sentence of reason and a pointer to the approved tool.
The approved route is now faster than the workaround, and the business can see what is used because it runs through an account the business controls. None of it needs a policy manual or a compliance department. It needs a conversation, a tool and a page.
What a ban does not change
Four things stay true whatever the rule says.
- The legal duties stay. Personal data entered into a tool the business has not assessed can breach its GDPR duties, and confidentiality clauses in client contracts apply whichever tool is used. The customer data article notes that buying a tool from a supplier does not remove the business’s own data protection duties.
- The task stays. A ban removes a route, not the reason people took it.
- Staff still need the reason. The use policy guide notes that the EU AI Act expects organisations that use AI to make sure their staff have a sufficient level of AI literacy, and says the Act’s wording in this area has been adjusted recently, so check the current text before quoting it. A short briefing is the practical evidence, and a prohibition alone does not supply it.
- Someone still has to own it. The ownership article reports that when nobody sets the rules, people set their own. A rule with no owner and no review date goes stale whether it permits or forbids.
Mix-ups worth avoiding
Four confusions come up often enough to name. The first is treating a ban as a policy. A ban is one possible line in a policy, and a policy that says only “no” is the blanket ban again. The second is treating a ban as the same thing as shadow AI, when the ban is a rule and shadow AI is what an unreviewed tool or account leaves behind. The third is treating an approved-tool list as a ban list. A list of what is approved says where to go, and a list of narrow bans says what to avoid and why, so a business needs both. The fourth is treating monitoring as a substitute for a rule. The accountancy survey found only 22% of workers said their employer actively monitors AI use, and monitoring cannot reach a personal phone.
How we use it
Every AI audit maps what each team actually uses, including the personal accounts and the AI features inside software the business already has. That map shows where a narrow ban is needed and where an approved tool would remove the reason for a workaround. The method asks before it audits and treats the answers as needs to meet, not as offences.
If you want to know what your teams are really using, and where a narrow rule would do more than a blanket one, a discovery call is a quick way to start.
Sources
- Why banning AI at work backfires, and what to do: the survey figures on bans, written policies, monitoring and entering work information into personal accounts, the reporting problem, the five steps that replace a ban and the four parts of a narrow ban.
- AI governance for small and mid-sized businesses: the unapproved-use figures that the shadow AI page reports.
- How to write an AI use policy for your team: the three-tier data rule, approved tools by version, and the AI literacy expectation under the EU AI Act.
- Customer data and AI tools: what is safe to paste: where a prompt goes, account type mattering more than brand, and the supplier not removing the business’s own data protection duties.
- What happens when nobody owns the AI you have rolled out: users setting the rules when nobody does, and the list of what is in use.
- How we audit: mapping what each team actually uses.
- Shadow AI, AI governance, AI tool inventory, AI ownership, Data protection, Data classification, AI literacy, GDPR and EU AI Act: the neighbouring terms this page links to.
FAQ
Questions about Ban on AI Tools
What is a ban on AI Tools?
A rule that forbids staff from using AI tools for work, either outright or tool by tool. A blanket ban removes the approved route but not the task, so use tends to move onto personal accounts the business cannot see.
Does banning AI Tools at work stop staff using them?
Usually not. A ban removes the tool but leaves the task, so a person with a deadline uses a personal account on a personal phone. A survey cited in our article found 28% of workers said they would use AI at work even if it were banned, and 38% in a separate survey admitted entering work information into a personal AI account.
How Common is an outright ban?
Rare. In a July 2026 survey of 500 US employees, cited in our article, only 6.6% said their employer bans AI tools outright, and 35.8% said there is a clear written policy. The usual situation is no rule at all, not a ban that staff ignore. These surveys are self-reported and were run by commercial firms, so read them as direction, not as precise measurement.
What should replace a blanket ban?
An approved tool on a business account that is good enough for daily work, and a one-page rule that says which kinds of data may never be entered, what is fine in the approved tool, and who to ask about anything else. Explain the reason for each line, ask each team what it needs without blame, and set an owner and a review date.
When is a ban still the Right call?
When it is narrow. A specific tool can be wrong for a specific kind of data, for example a consumer service that keeps what you enter when you handle client material under confidentiality. A good narrow ban names the tool or data, gives the reason, points to the approved alternative and says who to ask.
Is a ban the same as Shadow AI?
No, but one tends to cause the other. A ban is a rule. Shadow AI is AI used for work that the business has never approved or reviewed, such as a personal account on a consumer chatbot. A blanket ban removes the approved route, so the use carries on out of sight and becomes shadow AI.
What should a Narrow ban say?
Four things: the tool or the data it covers, the reason in one sentence, the approved alternative, and who to ask when a case is unclear. Keep the list short and dated, because the reason for a ban often expires when a tool changes its terms or an approved alternative appears.
Why banning AI at work backfires, and what to doAI Ownership
Does a ban protect a Business under GDPR?
Not by itself. Personal data entered into a tool the business has not assessed can still breach its duties, and a ban does not show that staff know where the line is. Our articles say buying a tool from a supplier does not remove the business's own data protection duties, and a rule people do not follow protects nobody. Take legal advice on your own contracts and sector.
What it means for a Business
Most small businesses have not banned AI; they have never said what is allowed. What works in place of a ban is an approved tool that is good enough for daily work, a one-page rule drawn by kind of data, and a short list of narrow bans that each name a tool or data, give a reason and point to an alternative.
Ready to Put This to Work?
Tell us where your team is with AI and we will tell you honestly what would make the biggest difference.